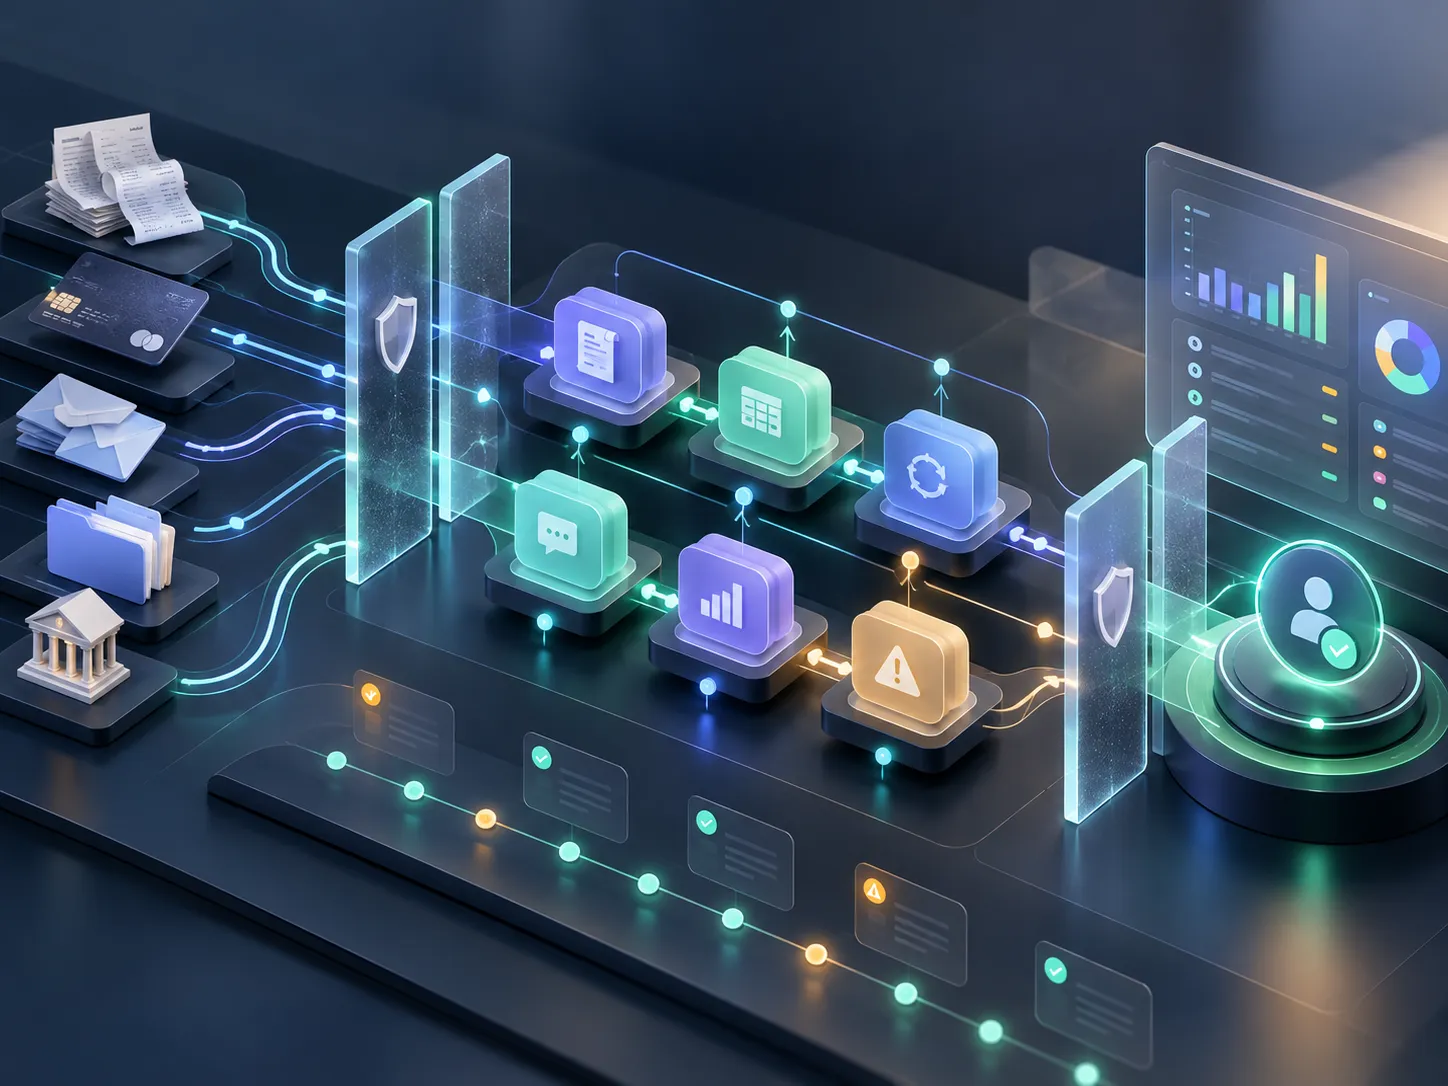
Financial automation needs boundaries you can explain.
dayBook is being designed around least privilege, reviewable actions, deterministic workers where possible, and hard limits where accounting or professional-discipline risk is higher.
Scoped access
Each worker or agent should have only the data and actions needed for its assigned job.
Workers before agents
When a task can be predictable and bounded, dayBook does not need to add open-ended AI judgment.
Human checkpoints
Draft coding, customer outreach, posting, and filing-sensitive work can stop for review before action.
Traceable context
Recommendations should retain enough source context to support review, correction, and investigation.
Data minimization
Collect and retain only the business information needed to operate the selected workflow.
Fail visibly
Exceptions, missing data, and failed handoffs should become visible work — not silent assumptions.
Trust accounts, IOLTA, filings, and other sensitive workflows are not a place to chase autonomy.
The planned product keeps trust and IOLTA workflows review-led, treats tax and regulatory items as preparation or watchlists rather than filing, and separates drafts from final human actions.